
French Supermarket Cyberattack Highlights the Importance of OT Security
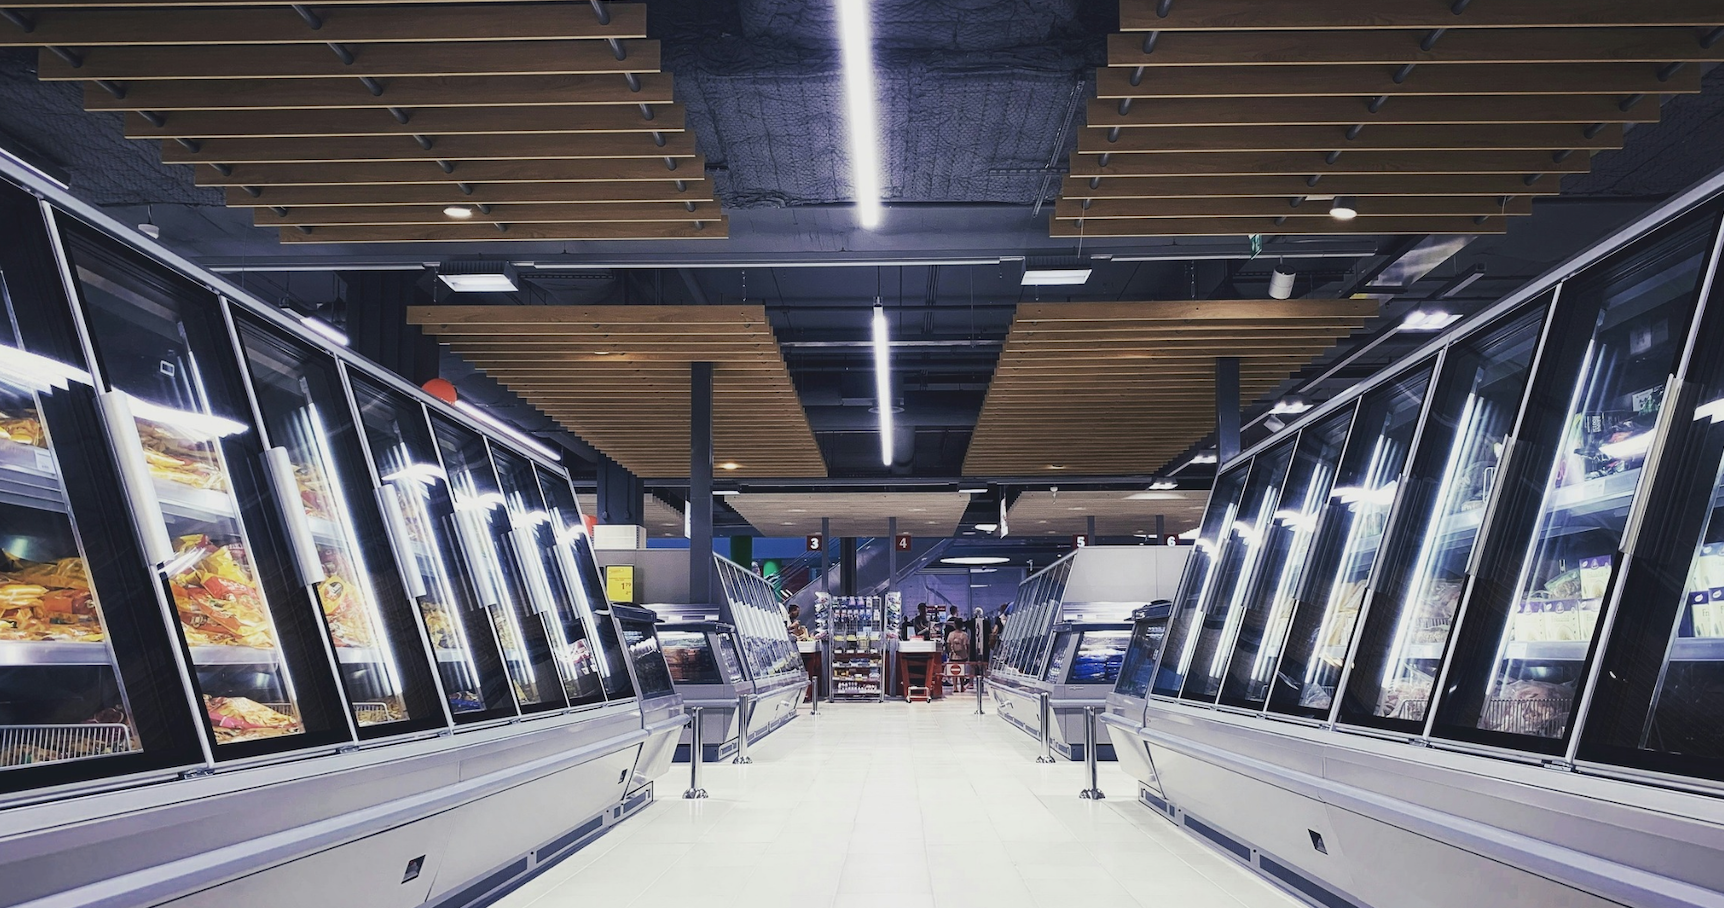
A cyberattack targeting connected refrigeration systems disrupted hundreds of supermarkets in France, spoiling fresh and frozen food. Some units reportedly reached 50°C for several hours, with fires also reported, according to BBC News and Reuters.
The incident affected equipment used to manage store refrigeration remotely. France’s cybersecurity authority is investigating and has warned that attacks may still be underway. Some reporting identified older refrigeration controllers from Danfoss, a Danish engineering company that supplies controls for commercial and industrial refrigeration systems. Danfoss said affected units were running outdated firmware, while the precise method used to access the systems has not been publicly established.
Why it matters
Refrigeration controls are operational technology: they manage physical processes businesses rely on every day. Remote access can make maintenance easier, but systems still need appropriate access protections, monitoring and a plan for security updates throughout their working life.
The incident is a practical reminder to include operational equipment in cybersecurity planning, even when it sits outside the usual office IT environment. IoT Insider’s coverage also highlights the challenge of managing connected devices after their software support ends. Denis Calderone, CTO at Suzu Labs, summarised the options for unsupported equipment: “segment it, monitor it, or replace it.”
Practical steps for businesses
Keep an up-to-date inventory of connected operational technology and its support status.
Restrict remote access to authorised users and secure connections.
Apply available firmware and security updates, and plan for equipment that has reached end of support.
Segment and monitor legacy devices; replace them where their risks can no longer be adequately managed.
Make sure IT, operations and suppliers know how to report and respond to unusual system behaviour.
The details of the attack remain under investigation. For organizations that depend on connected equipment, reviewing access, update and incident-response processes is a measured way to build resilience.